Skip to content

Revyz Command Center for Bitbucket

Secure every repository in your Bitbucket Cloud workspace — full git history and large files, pull requests, branch restrictions, permissions, deploy keys, webhooks and Pipelines configuration. Your single command center for source code security, compliance and control.

Bitbucket-Backup-Config-Management-Command-Center-for-Bitbucket-09-23-2026_10_17_AM

Command your Bitbucket : protect the code,
and the rules that govern it

Every developer has a copy of the code. Nobody has a copy of the permissions, the branch protections, the review policies or the pipeline configuration that decide who can ship it. Select a category below to see the modules that close that gap.

Backup & Restore
Backup & Granular Restore
Every branch, tag and commit plus Git LFS content, captured incrementally on your own schedule — and verified so a recovered repository clones cleanly rather than half-working. Take an on-demand checkpoint before a risky migration or an offboarding.
Optimize_Environment
Eight recovery scenarios
Repositories, branches and tags, settings and policy, access and integrations, CI and deployment, review state, project policy, workspace integrations. Real incidents are rarely "restore everything" — choose the narrowest write that fixes the problem.
Granular_Restore
Additive-only restore
No recovery deletes or overwrites code, history or branches. Work done since the backup survives. The worst outcome of choosing the wrong recovery point is that nothing is written — an inconvenience, not a second incident.
Third Party App Backup & Restore
Recover into a standby workspace
Restore into a connected or standby workspace to validate a recovery point before touching production, mapping users and groups from the old estate to the new one. The difference between believing you can recover and knowing it.
Deploy_Configuration
Configuration captured in full, every run
Repository settings and visibility, branching models, branch restrictions and their exemptions, default reviewers, and project-level policy — captured completely on every backup, not opportunistically. The change detection built for code is blind to configuration.
Config Drift Manager
The complete access model
Repository and workspace permissions, groups and group membership, deploy keys and webhooks — a full record of who could reach what, and when. Your backup becomes an access-review dataset, not just a recovery copy.
Deploy_Configuration
Configuration drift comparison
Compare any two points in time, or two workspaces against each other, and see exactly what was created, deleted or changed — with an export. A permission raised from write to admin shows as one clear change instead of disappearing into noise.
Extended_Audit
Audit trail and data residency
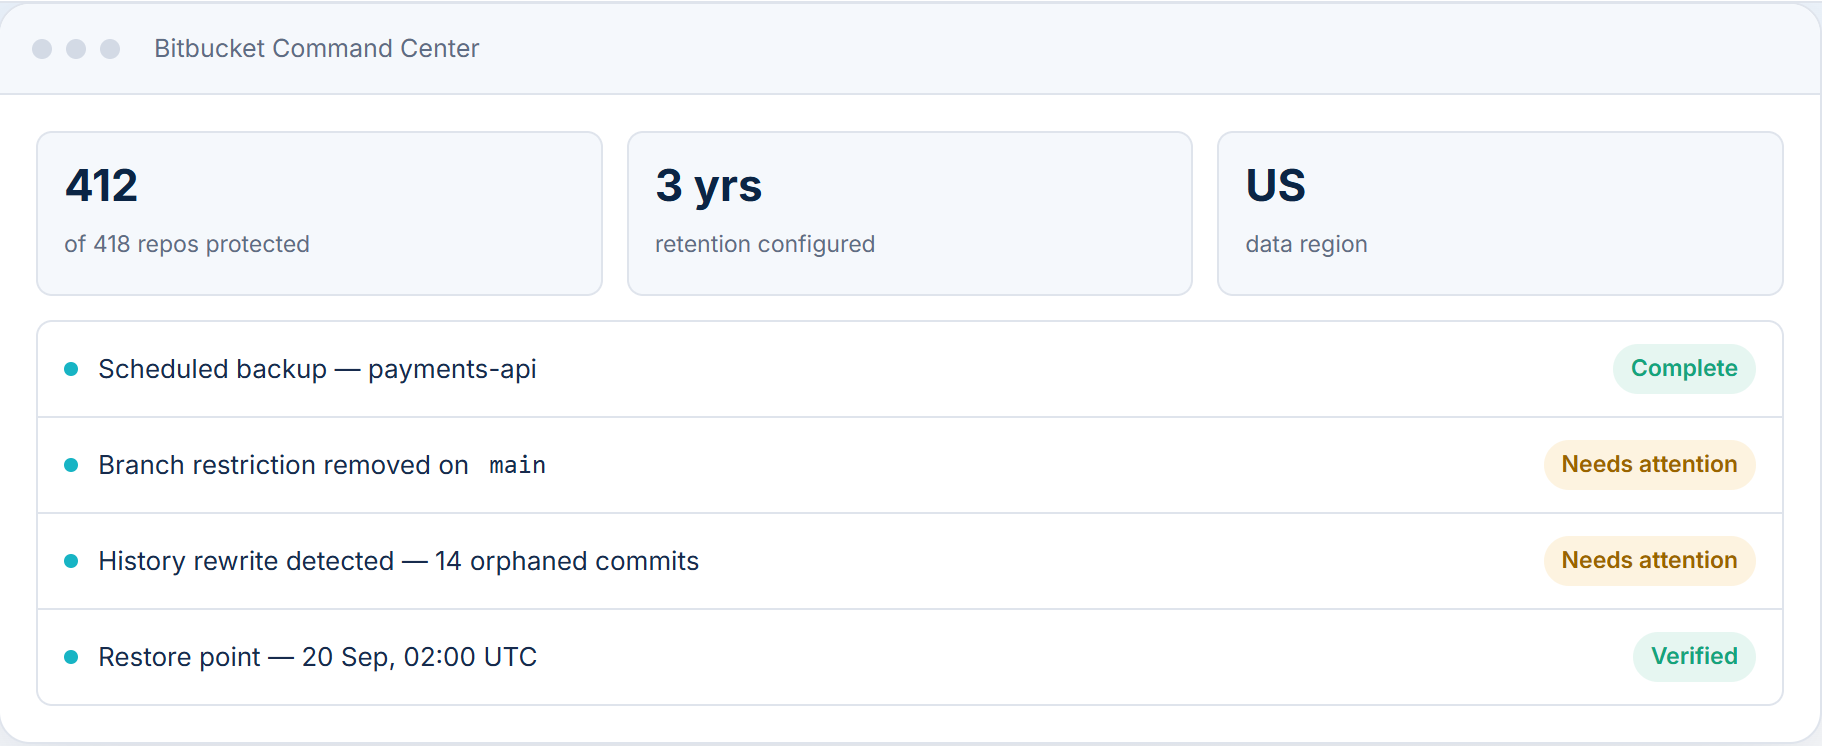
Every sign-in, permission change, invitation, configuration change, backup and restore is recorded and exportable by auditors themselves. Backup content, configuration, job records and job logs all stay in the region chosen at connection — United States or European Union.
User License Insights-2
Workspace Health — 21 built-in reports
Access reviews, protection scoring, dormancy, build waste, storage growth, file composition and seat activity. Ready to run, no configuration — governance reporting included rather than sold as a separate posture-management product.
Security_Compliance
Branch protection scoring
Which branches have no required approvals, allow force pushes, or can be deleted — scored and ranked across the whole estate, mapping directly to supply-chain security expectations and SDLC control evidence.
Enterprise_Controls
History rewrite and lost commit recovery
Detects when a branch's history has been rewritten, lists the commits it orphaned with author, date and message, and restores them safely to a new branch rather than force-pushing back.
Optimize_Environment
Reporting that costs your team nothing
Reports run against the backup, so they never consume the API capacity your developers rely on and never need write access to the live workspace. Posture tools that hammer the live API get switched off; this one doesn't.
Protect what a clone can't
A repository is a folder of files wrapped in a set of decisions — who may write to main, how many approvals a change needs, which service accounts hold keys, which pipeline variables make the build work at all. None of that is in anybody's clone, and all of it can be changed in seconds by one person with admin rights.
One platform across your Atlassian estate
The same console that protects Jira, Jira Service Management, Assets and Confluence now protects Bitbucket Cloud. One vendor, one interface, one support team, one security review — instead of a separate point tool for every product your teams depend on.
Backup that earns its keep weekly
The dataset needed to protect a workspace is the same dataset needed to govern one. Access reviews, branch protection scoring and drift comparison turn a policy you pay for into a tool your admins open on a Tuesday — not insurance you hope never to claim.

No recovery deletes or overwrites code or history. Every restore writes only what is missing.

The conventional model — make the destination match the backup — means a restore run against a live workspace deletes anything the backup doesn't know about. Every branch created since. Every commit pushed this morning. In a recovery, where someone is already stressed and guessing at which restore point is right, that model turns a mistake into a second incident.

  • A design property, not a setting. There is no force option anywhere in the product to turn it off.
  • A plain-language preview before the write. Exactly what will be created, what will be replaced, and what side effects to expect — including that restoring a schedule may start a build tonight.
  • Identity re-verified at the point of restore. A fresh check at the moment of the write, not a login from three hours ago. No classification, no way to skip it.
  • A line for every object. Written, skipped or refused, and why — with the previous value recorded wherever something was replaced. That report is what your post-incident review runs on.
  • Cancel a running recovery. Stop a restore mid-flight safely — cancelling can never leave a half-destroyed destination.

Enterprise-grade security for a second copy of your crown jewels

Buying a backup product means handing a complete, continuously updated copy of your intellectual property to a third party. Done carelessly, that is not a security improvement. These are the controls that make it a net gain.

  • SOC 2 Type II certified, with a deliberately short subprocessor list and a standard DPA
  • Customer-dedicated encryption keys — per workspace, not per vendor tenancy
  • Encrypted by the application before it reaches storage, so the storage layer never holds readable source code
  • Secrets are never captured — pipeline secrets, webhook signing secrets and private key material are excluded by design; deploy keys are recorded by fingerprint and label only
  • Mandatory multi-factor authentication for every user in every role, with no opt-out and no administrative exception
  • A two-dimensional role model — what a person may do, and which workspaces they may reach
  • A genuinely read-only auditor role, so gathering evidence never requires issuing admin rights
  • Permissions enforced on every request, with immediate session revocation when an account is deactivated
  • Workspace isolation at the identity, storage and key layers independently
  • Regional data residency covering content, configuration, job records and job logs — the exception most vendors forget to mention
  • Retention from one to seven years, with expiry and genuine erasure kept as separate, audited operations
  • Protection is never gated on a plan limit — a commercial dispute must never become a data-loss event

Trusted by the Best in the Business

Revyz helps enterprise IT, infrastructure, and security & compliance leaders manage Atlassian Cloud with confidence, ensuring security and compliance.

 
Nicole EksteenDigital Transformation Director, Avior Capital Markets

Highly recommend Revyz. The app is secure, easy to use, and backed by a responsive support team. If you manage a growing or complex Jira environment, Revyz is an incredibly valuable tool that brings peace of mind and operational efficiency.

Laurens CoppensBusiness Unit Manager, Axians Belgium

Backup is great and at its core, but the fact that it also gives you optimise and analyse functionalities is amazing. I can highly recommend this app to anyone who wants to sleep better at night and not worry about their data.

Kyle MoseleyCEO, Blue Ridge Consultants

We're really loving this app, it's very reliable and the team developing it is quick to add features. Support is very quick with responses when we've reached out.

Capability
Revyz Data Manager
Salto
Audit Log Retention Period
3 yrs with Revyz storage,
Unlimited with your own storage
Immutable, Tamper-Proof Storage

Comprehensive coverage for your Bitbucket Cloud workspace

The list of what is not covered is short, and it is published. Everything below is captured on every protected repository.
Compare_Clone Repositories Branches, tags, commits and Git LFS content  
Enterprise_Controls Pull requests Open, merged, declined and superseded  
Deploy_Configuration Pipelines Configuration, environments, variables and schedules  
Version_Control Projects & workspaces Policy, members, runners, snippets and downloads  

See the Unified Platform in Action

Discover how Revyz can transform your Atlassian security and compliance strategy. Schedule a free, no-obligation demo with our experts today.